Focusing on attacker behavior rather than static signatures reveals threats that traditional tools miss, allowing for earlier detection and more accurate response.
TTPs describe the specific methods attackers use to move through a network, allowing defenders to detect behavior rather than just known file signatures.
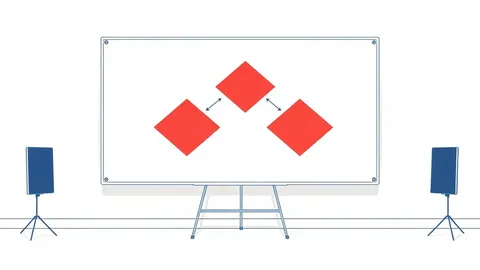
The Diamond Model forces you to track adversary capabilities and infrastructure, revealing why blocking one attack vector fails when the attacker pivots to another.
Most long-term intrusions succeed because defenders focus on initial access rather than the quiet persistence mechanisms that allow attackers to survive system reboots and patching cycles.