Threat Intelligence
Implement Deception Technology: A Step-by-Step Operational Guide
Deception technology shifts detection from monitoring normal behavior to triggering immediate alerts on any interaction with fake assets.
Threat Intelligence coverage from SecOps Monitor holds 19 articles, 18 of them reference guides. The newest was published on October 14, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include MITRE ATT&CK and MITRE D3FEND.
Deception technology shifts detection from monitoring normal behavior to triggering immediate alerts on any interaction with fake assets.
Attackers exploit the Kerberos pre-authentication bypass to harvest ticket-granting tickets offline, allowing them to crack credentials without triggering standard authentication logs on the domain controller.
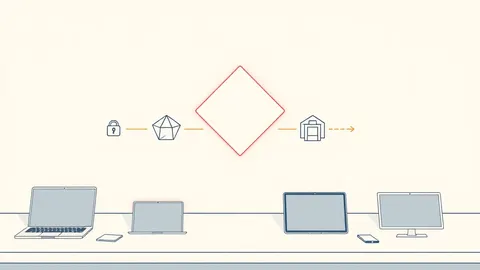
The Diamond Model reveals hidden links between attacker tools and victim systems that traditional log analysis often misses entirely.
Incident triage determines which alerts require immediate human intervention, preventing response teams from burning out on noise while missing critical intrusions.
Attackers modify system records to hide their presence, making it impossible to distinguish normal activity from malicious behavior without external verification.
A Check Point bulletin highlights supply chain risks, stolen credentials, and AI-augmented attacks targeting government and retail sectors across multiple continents.
Understanding the specific financial or ideological motive behind an attack allows you to predict the next move before the breach completes.
Focusing on attacker behavior rather than static signatures reveals threats that traditional tools miss, allowing for earlier detection and more accurate response.
TTPs describe the specific methods attackers use to move through a network, allowing defenders to detect behavior rather than just known file signatures.
The Diamond Model forces you to track adversary capabilities and infrastructure, revealing why blocking one attack vector fails when the attacker pivots to another.
Process injection hides malicious code inside legitimate system processes, making it invisible to tools that only monitor new process creation events.
Honeypots generate noise that masks real attacks unless you isolate them and filter their traffic before it reaches your primary security tools.
Packet capture reveals the raw truth of network behavior, exposing hidden protocols and data exfiltration attempts that firewall logs consistently miss.
DCSync attacks leave no file changes and no registry edits, making behavioral log analysis the only reliable detection method for credential harvesting.
Profiling reveals the attacker’s operational rhythm and resource constraints, allowing you to disrupt campaigns by targeting their weakest logistical link rather than just patching vulnerabilities.
Security and network operations centers serve different purposes; confusing their distinct alert thresholds causes critical security events to get buried in routine performance noise.
Most long-term intrusions succeed because defenders focus on initial access rather than the quiet persistence mechanisms that allow attackers to survive system reboots and patching cycles.
Clarify the mechanical difference between event correlation and automated response, ensuring you deploy each tool for its specific operational purpose rather than overlapping functions.
You will learn how to weigh detection gains against operational noise and decide when simulation adds value to your security posture.