Threat Intelligence
Process Injection: How It Works and How to Detect It
Process injection hides malicious code inside legitimate system processes, making it invisible to tools that only monitor new process creation events.
Process injection hides malicious code inside legitimate system processes, making it invisible to tools that only monitor new process creation events.
Honeypots generate noise that masks real attacks unless you isolate them and filter their traffic before it reaches your primary security tools.
Misconfigured lockout thresholds turn routine password errors into a denial-of-service weapon that shuts down your entire authentication infrastructure.
Packet capture reveals the raw truth of network behavior, exposing hidden protocols and data exfiltration attempts that firewall logs consistently miss.
Memory-safe languages eliminate entire classes of vulnerabilities by managing memory access rules at compile time, removing the burden from manual code reviews.
Updating dependencies often introduces new attack surfaces and configuration drift that outweigh the security benefit of closing known flaws.
Every API request undergoes a sequential authorization check that can silently fail if role bindings are misconfigured or if service accounts inherit unintended permissions.
Most training fails because it targets memory rather than behavior, ignoring the cognitive biases attackers exploit during high-pressure moments.
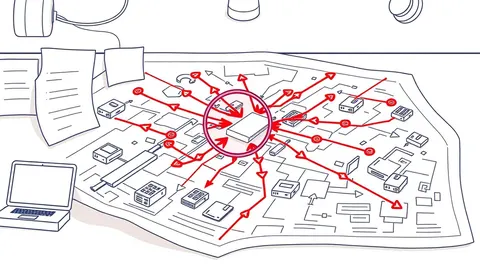
Threat modeling prevents architectural blind spots by forcing you to map data flow before code exists, though it cannot replace runtime detection.
Attackers bypass perimeter defenses by stealing session tokens and identity assertions, rendering traditional network security controls irrelevant.
DCSync attacks leave no file changes and no registry edits, making behavioral log analysis the only reliable detection method for credential harvesting.
Personal posts expose internal network structures and employee habits, giving attackers the context needed to bypass technical security controls.
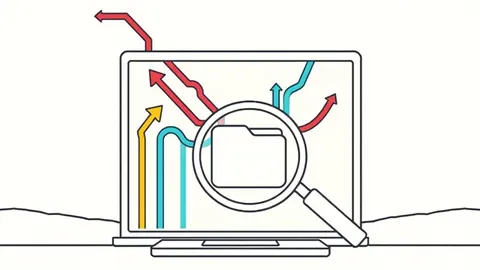
A firewall controls traffic flow at the network boundary, while antivirus software scans files on the host for known malicious signatures, addressing entirely different attack vectors.
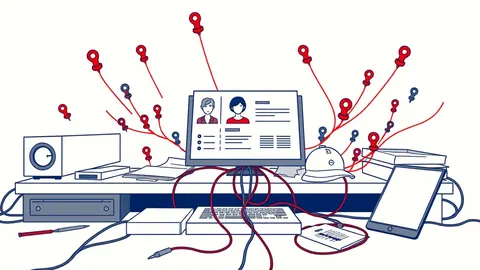
Profiling reveals the attacker’s operational rhythm and resource constraints, allowing you to disrupt campaigns by targeting their weakest logistical link rather than just patching vulnerabilities.
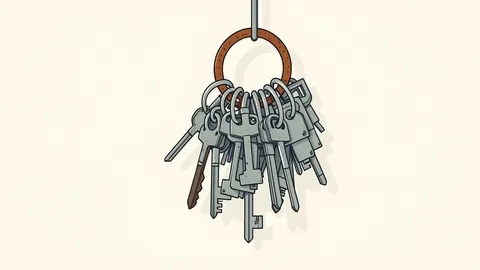
Identity sprawl often hides in dormant service accounts and stale group memberships, creating silent backdoors that standard audits miss entirely.
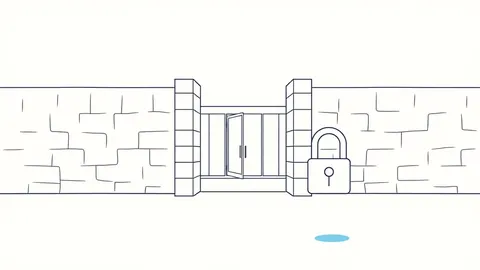
Traditional VPNs grant broad network access based on location, while zero trust verifies every request regardless of where it originates.
Just-in-time access reduces the attack surface by granting privileges only during active work, but it introduces latency and operational friction that can hinder emergency response.
Cryptojacking often bypasses traditional security by exploiting trust relationships and legitimate administrative tools rather than breaking encryption or stealing data.
Dynamic testing finds logic flaws that static scanners miss, but it requires a dedicated test environment to prevent accidental data loss or service disruption.
Exposed storage buckets often remain silent in network logs because attackers use standard HTTPS, hiding their activity behind legitimate traffic patterns.
Cryptographic nonces prevent attackers from using captured data packets to impersonate legitimate users or trigger duplicate actions.
Default router settings expose internal networks to external attacks, requiring specific configuration changes to prevent unauthorized access.
Memory-safe languages enforce ownership rules at compile time, eliminating entire classes of memory corruption vulnerabilities without requiring runtime garbage collection overhead.
Signature scanning catches known threats instantly but remains blind to new code, creating a false sense of security that leaves zero-day exploits undetected.